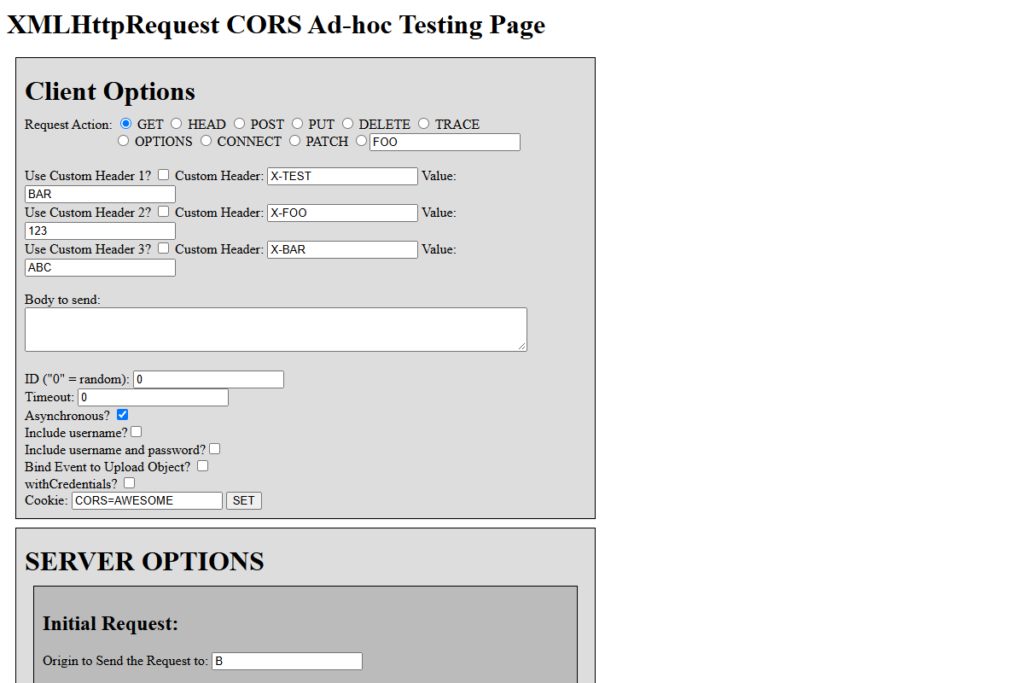
I made a testing page for cross-origin requests in IE10 and Windows 8. CORS is one of those things where a tiny difference in a header can completely change what the browser lets you do. I wanted to be able to change one thing at a time and actually see what happened.
The client uses XMLHttpRequest and logs ready-state changes, load and error events, response headers, and timing. There are switches for credentials, custom headers, request methods, timeouts, and redirects. A PHP endpoint supplies the other half of the experiment, including allowed and disallowed origins and preflight responses.
One useful case is the difference between allowing any origin and allowing credentials: a wildcard origin is not permission to send cookies. The page also lets me check which response headers JavaScript can actually read. Not the prettiest project, but much nicer than repeatedly editing the same test by hand.